
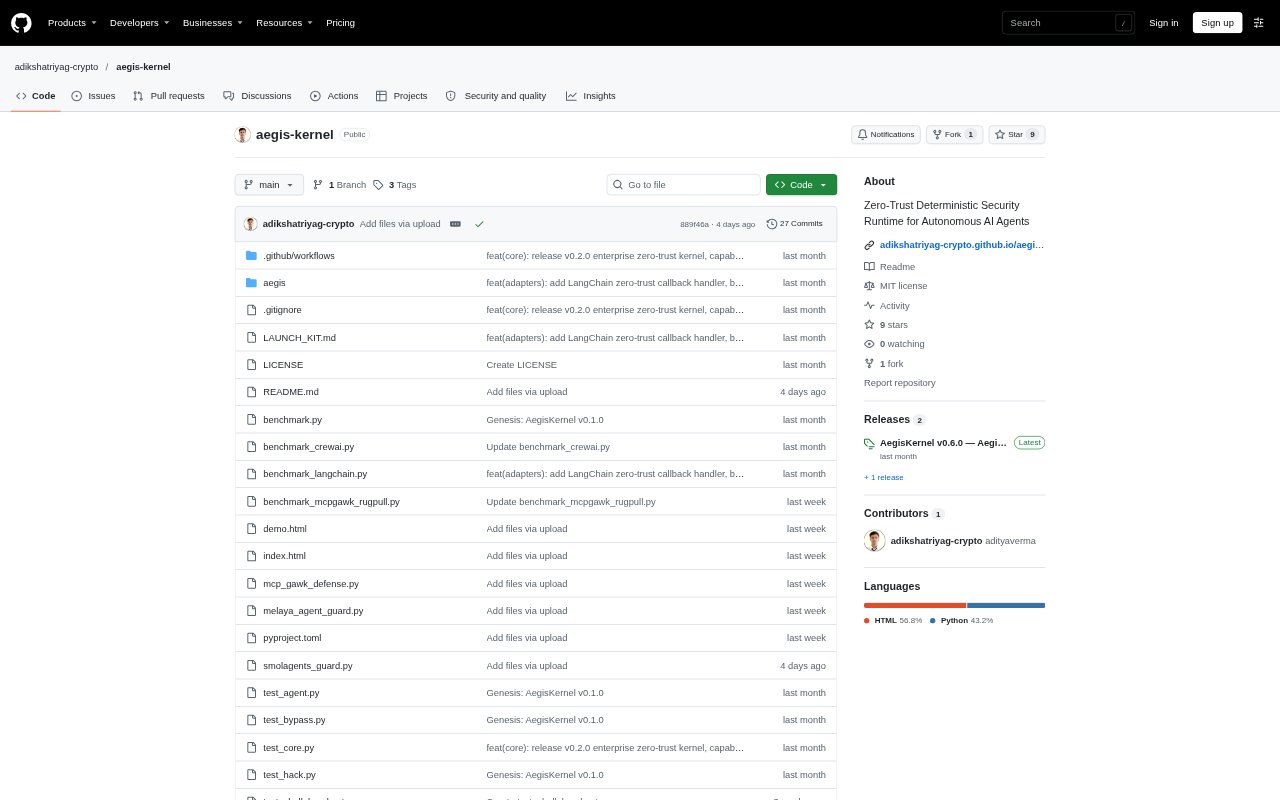
What is AegisKernel?
AegisKernel is a Python security runtime for autonomous AI agents and agent tools that can access files, databases, or shell commands. It applies capability-based rules at tool execution time, limiting what a tool can do within a task-scoped boundary. Developers can wrap individual functions or protect existing CrewAI and LangChain agents, and it also provides an approach for sandboxing MCP tools and local smolagents execution.
AegisKernel Features:
Capability Policies: Security policies grant tools explicit capabilities, such as file-read access, and can restrict filesystem access to specified paths.
Tool Interception: The protect_tool wrapper intercepts agent tool invocations and checks whether their execution stays within the configured capability boundary.
Path Sandboxing: Deterministic path sandboxing restricts filesystem operations to task-scoped roots, including attempts to traverse outside an allowed path.
Shell Restrictions: The runtime blocks interactive subshell spawning and destructive binaries before execution through execve.
Agent Integrations: Integration helpers protect existing CrewAI and LangChain agents, while the runtime can also wrap MCP and smolagents tools.
Local Web Sandbox: An interactive browser sandbox lets developers try capability enforcement, and the project also provides a local demo.
AegisKernel Benefits:
Reduced Exposure: Confining tools to task-specific access can limit the damage if an agent is manipulated into making an unsafe request.
Lower Check Overhead: Deterministic checks avoid adding a secondary LLM call to each tool invocation, along with its associated latency and API cost.
Clearer Boundaries: Explicit capabilities make it easier for developers to reason about what an agent tool is permitted to do.
Faster Integration: Wrapping existing tool functions or supported agents offers a direct way to add execution checks to an agent workflow.
Open Source Access: The MIT-licensed project is available for teams to inspect, use, and adapt in their own agent development.
Use Cases:
Agent File Access: Restrict an agent that reads workspace data so it cannot use path traversal to reach files such as environment or SSH keys.
Shell Tool Control: Add execution boundaries to an agent tool that runs shell commands, including protection against interactive subshells and destructive binaries.
MCP Tool Sandboxing: Limit an MCP file-reading tool to an explicit capability so a request for a path outside its scope is rejected.
CrewAI and LangChain: Protect an existing CrewAI or LangChain agent when its tools can access a filesystem, database, or terminal.
smolagents Workspaces: Confine a local smolagents CodeAgent to a designated workspace when it executes Python code.