
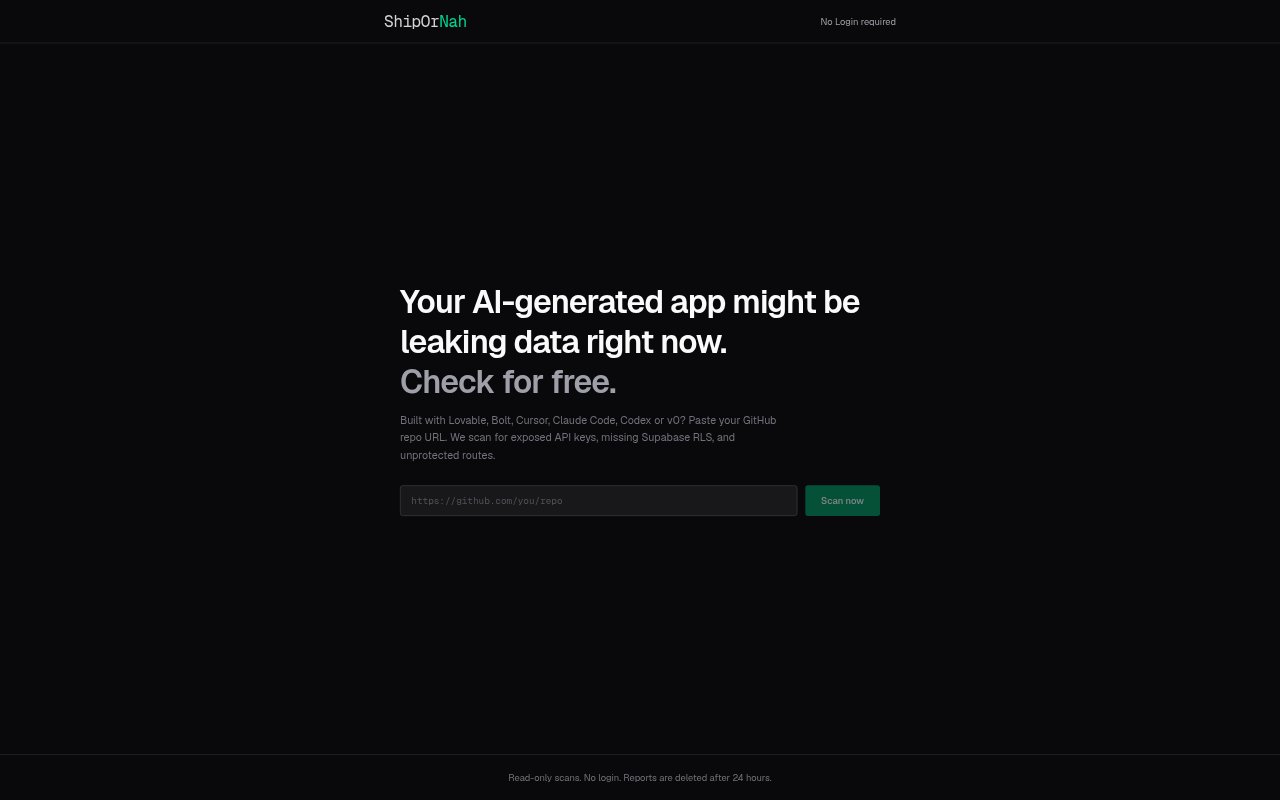
What is ShipOrNah?
ShipOrNah is a free security scanner for apps built with AI coding tools, including Lovable, Bolt, Cursor, Claude Code, Codex, and v0. You provide a GitHub repository URL, and it checks for exposed API keys, missing Supabase row-level security policies, and routes that lack protection. It is intended for people building AI-generated apps who want to check for these security issues in their code, rather than a general-purpose app builder or a tool that creates the app for them.
ShipOrNah Features:
Free Security Scan: The app security scan is offered for free, so you can check a project without needing a paid plan for this listed capability.
GitHub Repository Input: To start a scan, provide the GitHub repository URL for the app you want checked.
API Key Checks: The scan looks for exposed API keys in an app, helping surface credentials that may be visible in the project.
Supabase RLS Checks: ShipOrNah checks for missing Supabase row-level security policies, a specific database security concern for apps using Supabase.
Route Protection Checks: The scan checks for unprotected routes, bringing attention to app routes that may not have access protection.
AI Builder Coverage: It is aimed at apps built with Lovable, Bolt, Cursor, Claude Code, Codex, or v0, rather than one named builder alone.
ShipOrNah Benefits:
Spot Credential Exposure: Checking for exposed API keys gives builders a way to notice a credential risk while reviewing an AI-generated app.
Review Data Access: A Supabase RLS check can help you identify a missing policy that could leave database access controls incomplete.
Check Route Access: Finding unprotected routes helps you focus a security review on places where access protection may be absent.
Focus Your Review: The scan concentrates on three named security concerns, giving you specific areas to examine instead of an unspecified general review.
Check Without a Fee: Because the scan is free, you can run this listed check without a stated scanning charge.
Use Cases:
Review an AI App: After building an app with Lovable, Bolt, Cursor, Claude Code, Codex, or v0, submit its repository to check for the listed issues.
Check API Credentials: When reviewing an app repository, use the scan to look for API keys that may be exposed in the project.
Inspect Supabase Security: For an app that uses Supabase, check whether the project has missing row-level security policies.
Review Protected Routes: When assessing app routes, use the scan to look for routes that may not have protection in place.
Check Before Release: Before making an AI-generated app available to users, submit its GitHub repository to check for exposed keys, missing Supabase RLS, and unprotected routes.