
What is SkillTotal?
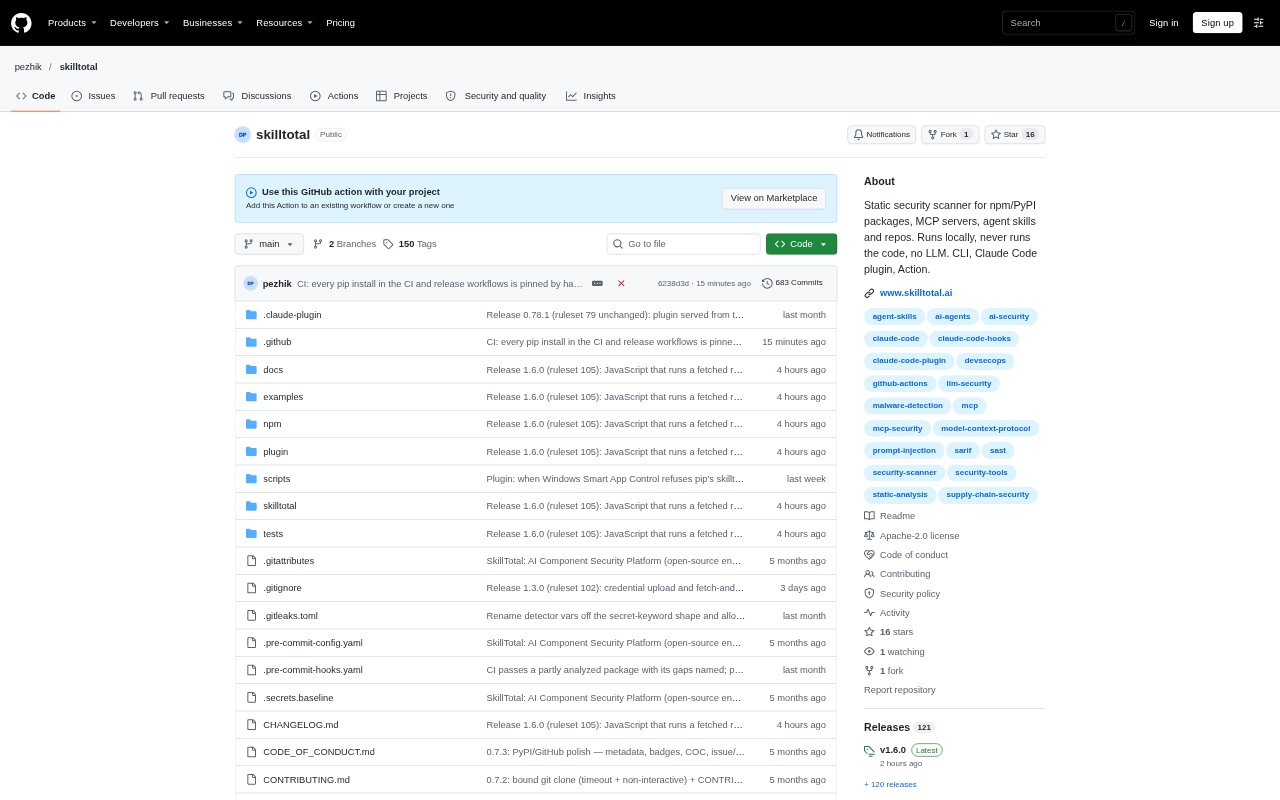
SkillTotal is a static security scanner for npm and PyPI packages, MCP servers, agent skills and plugins, and code repositories. It examines component files for risky behavior, prompt-injection surfaces and possible data exfiltration without running the code or using an LLM. Developers can scan locally with the CLI, check components through the web scanner, or add checks to an agent workflow or CI pipeline. Reports include a risk score and findings linked to file and line evidence.
SkillTotal Features:
Component Scanning: Scan packages, repositories, local folders, archives and individual files, including MCP servers, agent skills, plugins and VS Code extensions.
Risk Detection: Look for shell execution, sensitive file access, network egress, install-time scripts, dynamic code execution, obfuscation and prompt-injection language.
Evidence Reports: Review findings with file, line range and code snippet evidence, alongside a risk score from 0 to 100 and a risk level.
Behavior Mapping: Findings include OWASP Agentic Skills Top 10 identifiers where applicable, while behavior traits reference CSA, MAESTRO and MITRE ATLAS.
Report Exports: Export scan results as JSON or SARIF for further review or use in security workflows.
Install Checks: The Claude Code plugin scans packages before install commands run, while a GitHub Action can gate pull requests on scan results.
Deep Analysis: A separate server-side analysis option offers LLM verification, exploitability and impact analysis, dynamic analysis in an isolated sandbox, and remediation guidance.
SkillTotal Benefits:
Safer Reviews: Teams can inspect potential risks before trusting a component or adding it to a project.
Focused Investigation: Code-level evidence gives reviewers a starting point for checking why a finding appeared and what it affects.
Consistent Results: Deterministic scanning makes findings easier to compare across repeated checks of the same component.
Private Local Scans: Running the open-source scanner locally keeps scanned code on the user's machine and requires no account, token or LLM key.
Lower Review Friction: Automated checks in agent installs and CI let teams include security review in existing development steps.
Use Cases:
Agent Package Review: Check an npm or PyPI dependency before approving a coding agent's request to install it.
MCP Server Vetting: Review an MCP server's exposed capabilities and potential access to shells, files, networks or credentials before adoption.
Pull Request Gate: Run a scan in CI and fail a pull request when findings meet a chosen risk threshold.
Dependency Upgrade: Compare a proposed dependency upgrade with the current version and identify newly introduced findings before merging.
Installed Tool Review: Check MCP servers, plugins, skills and editor extensions already installed on a workstation or company fleet.