
What is Vericto?
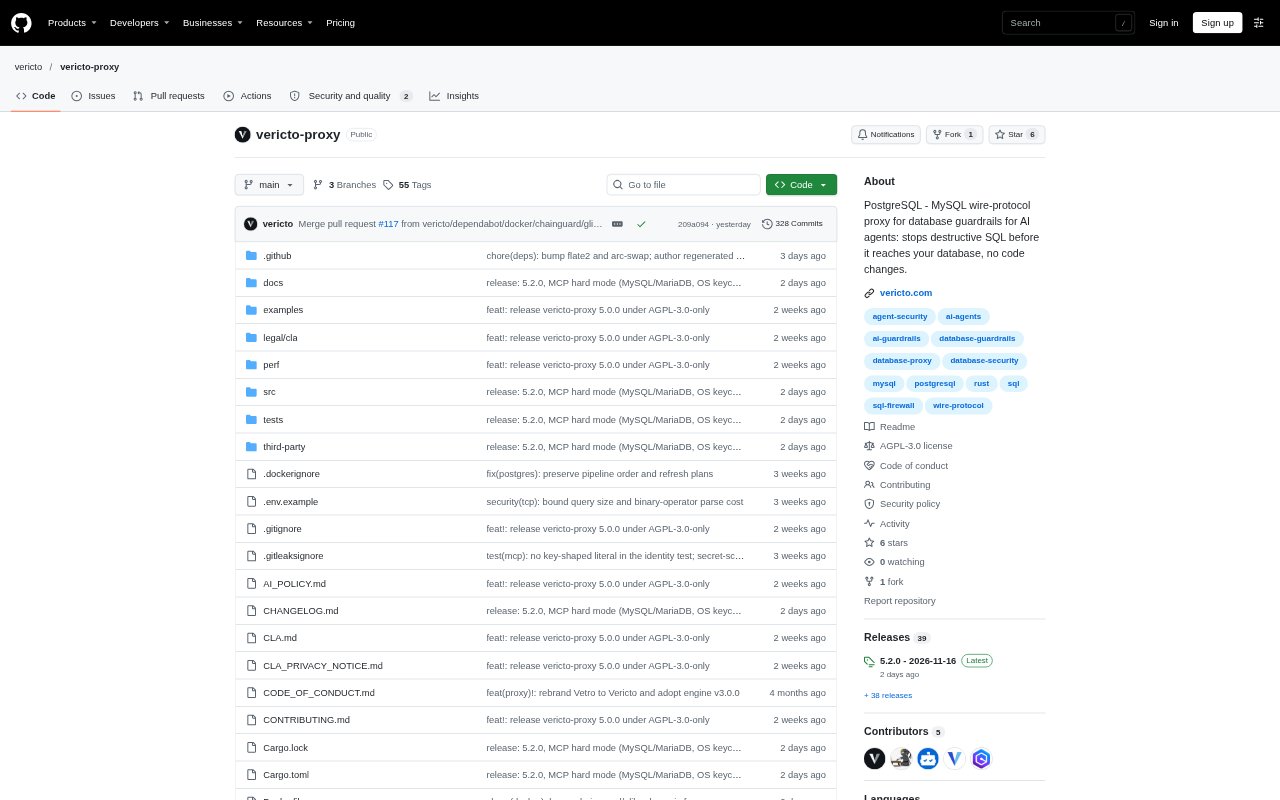
Vericto is a database guardrail tool for teams that connect AI agents, applications, scripts, or people to databases. It checks SQL against rules before a query reaches the database, then allows it, blocks it with a suggested fix, or masks sensitive results. Teams can use it through a proxy, API, CLI, or MCP integration, with the proxy supporting PostgreSQL and MySQL and other SQL dialects available through API, CLI, or MCP.
Vericto Features:
AST Rule Checks: Vericto parses SQL into an abstract syntax tree and evaluates statements against built-in rules, including rules against destructive queries and tautological conditions.
Database Proxy: The TCP proxy sits between clients and PostgreSQL or MySQL, forwarding allowed queries and returning a native database error when a rule blocks one.
MCP for Agents: The proxy provides execute_sql and check_sql tools for coding agents, including Claude Code, Cursor, and LangChain, while keeping the database connection string with the proxy.
CI SQL Checks: The CLI and check-sql action inspect changed SQL files in a pull request and can annotate findings on the diff or fail a pipeline.
Sensitive Data Masking: On Team and Enterprise plans, tagged sensitive columns can be masked, flagged, or blocked, with the proxy rewriting masked query results before they reach the client.
Policies and Audit: Teams can create policies, observe queries before enforcing rules, use a kill switch, and record decisions in an audit trail with signed reports.
Vericto Benefits:
Fewer Accidental Changes: Blocking risky statements before execution helps reduce the chance that a missing filter or destructive command alters production data.
Actionable SQL Feedback: A blocked statement comes with the rule that triggered it and a suggested fix, giving an agent or developer a concrete next step.
Less Integration Work: Applications can route connections through the proxy by changing the host and port, without changing their SQL code or requiring a special driver.
Reduced Data Exposure: Masking or blocking selected columns helps limit sensitive values included in query results sent to an agent or application.
Reviewable Decisions: Recorded query decisions and signed reports give teams material to review database activity and support audit preparation.
Use Cases:
AI Database Agents: Add a check before an AI agent runs generated SQL, such as preventing a DELETE without a WHERE clause from reaching a production database.
Migration Pull Requests: Run checks on changed SQL files in CI so a destructive migration can be surfaced or stopped before deployment.
Text-to-SQL Apps: Route queries from a natural-language database interface through Vericto to check them before execution and control access to tables and columns.
Personal Data Access: Configure rules for database columns containing details such as email addresses or card numbers when query results may enter an LLM context.
Audit Preparation: Use the decision trail and signed reports when assembling evidence for SOC 2 or ISO 27001 audit work.